
In this article
- What is the EU AI Act?
- When does each part of the EU AI Act apply?
- Which risk classes does the EU AI Act have?
- Are you a provider or a deployer?
- What does AI literacy ask of your business?
- Where do the GDPR and the EU AI Act overlap?
- How do you tackle the EU AI Act in four steps?
- What should you watch with ChatGPT and other public models?
- What does the EU AI Act mean for AI agents?
- When can you take this lightly?
- Who supervises the EU AI Act and what are the fines?
- What should you do now, and what can wait?
- Checklist: the EU AI Act for SMEs
- Frequently asked questions
Your people already use AI. In a chat window, in a summary, in a tool someone switched on without asking. So the question is not whether you need to deal with it, but whether you can show what happens to which data. Two sets of rules decide that: the GDPR, which has applied for years, and the EU AI Act, which comes into force step by step.
Those steps shifted in July 2026. The heavy rules for high-risk AI now apply from 2 December 2027 instead of August 2026. However, that is no reason to wait. AI literacy has applied since February 2025, and what you map out now, you will not have to do in a rush later. This article gives you a way of working, not legal advice. Check your approach with your data protection officer or a lawyer.
What is the EU AI Act?
The EU AI Act is the European law that sets rules for developing and using AI systems, based on risk. The bigger the risk to people, the heavier the requirements. A small number of uses is banned, one group counts as high risk, and for most uses only light rules apply.
Its official name is Regulation (EU) 2024/1689 (EUR-Lex). In July 2026 the EU amended it with the so-called Digital Omnibus, Regulation (EU) 2026/1744 (EUR-Lex). That amendment mainly moved the dates for high risk. Also, a regulation applies directly across the whole EU, so it needs no national law to take effect.
When does each part of the EU AI Act apply?
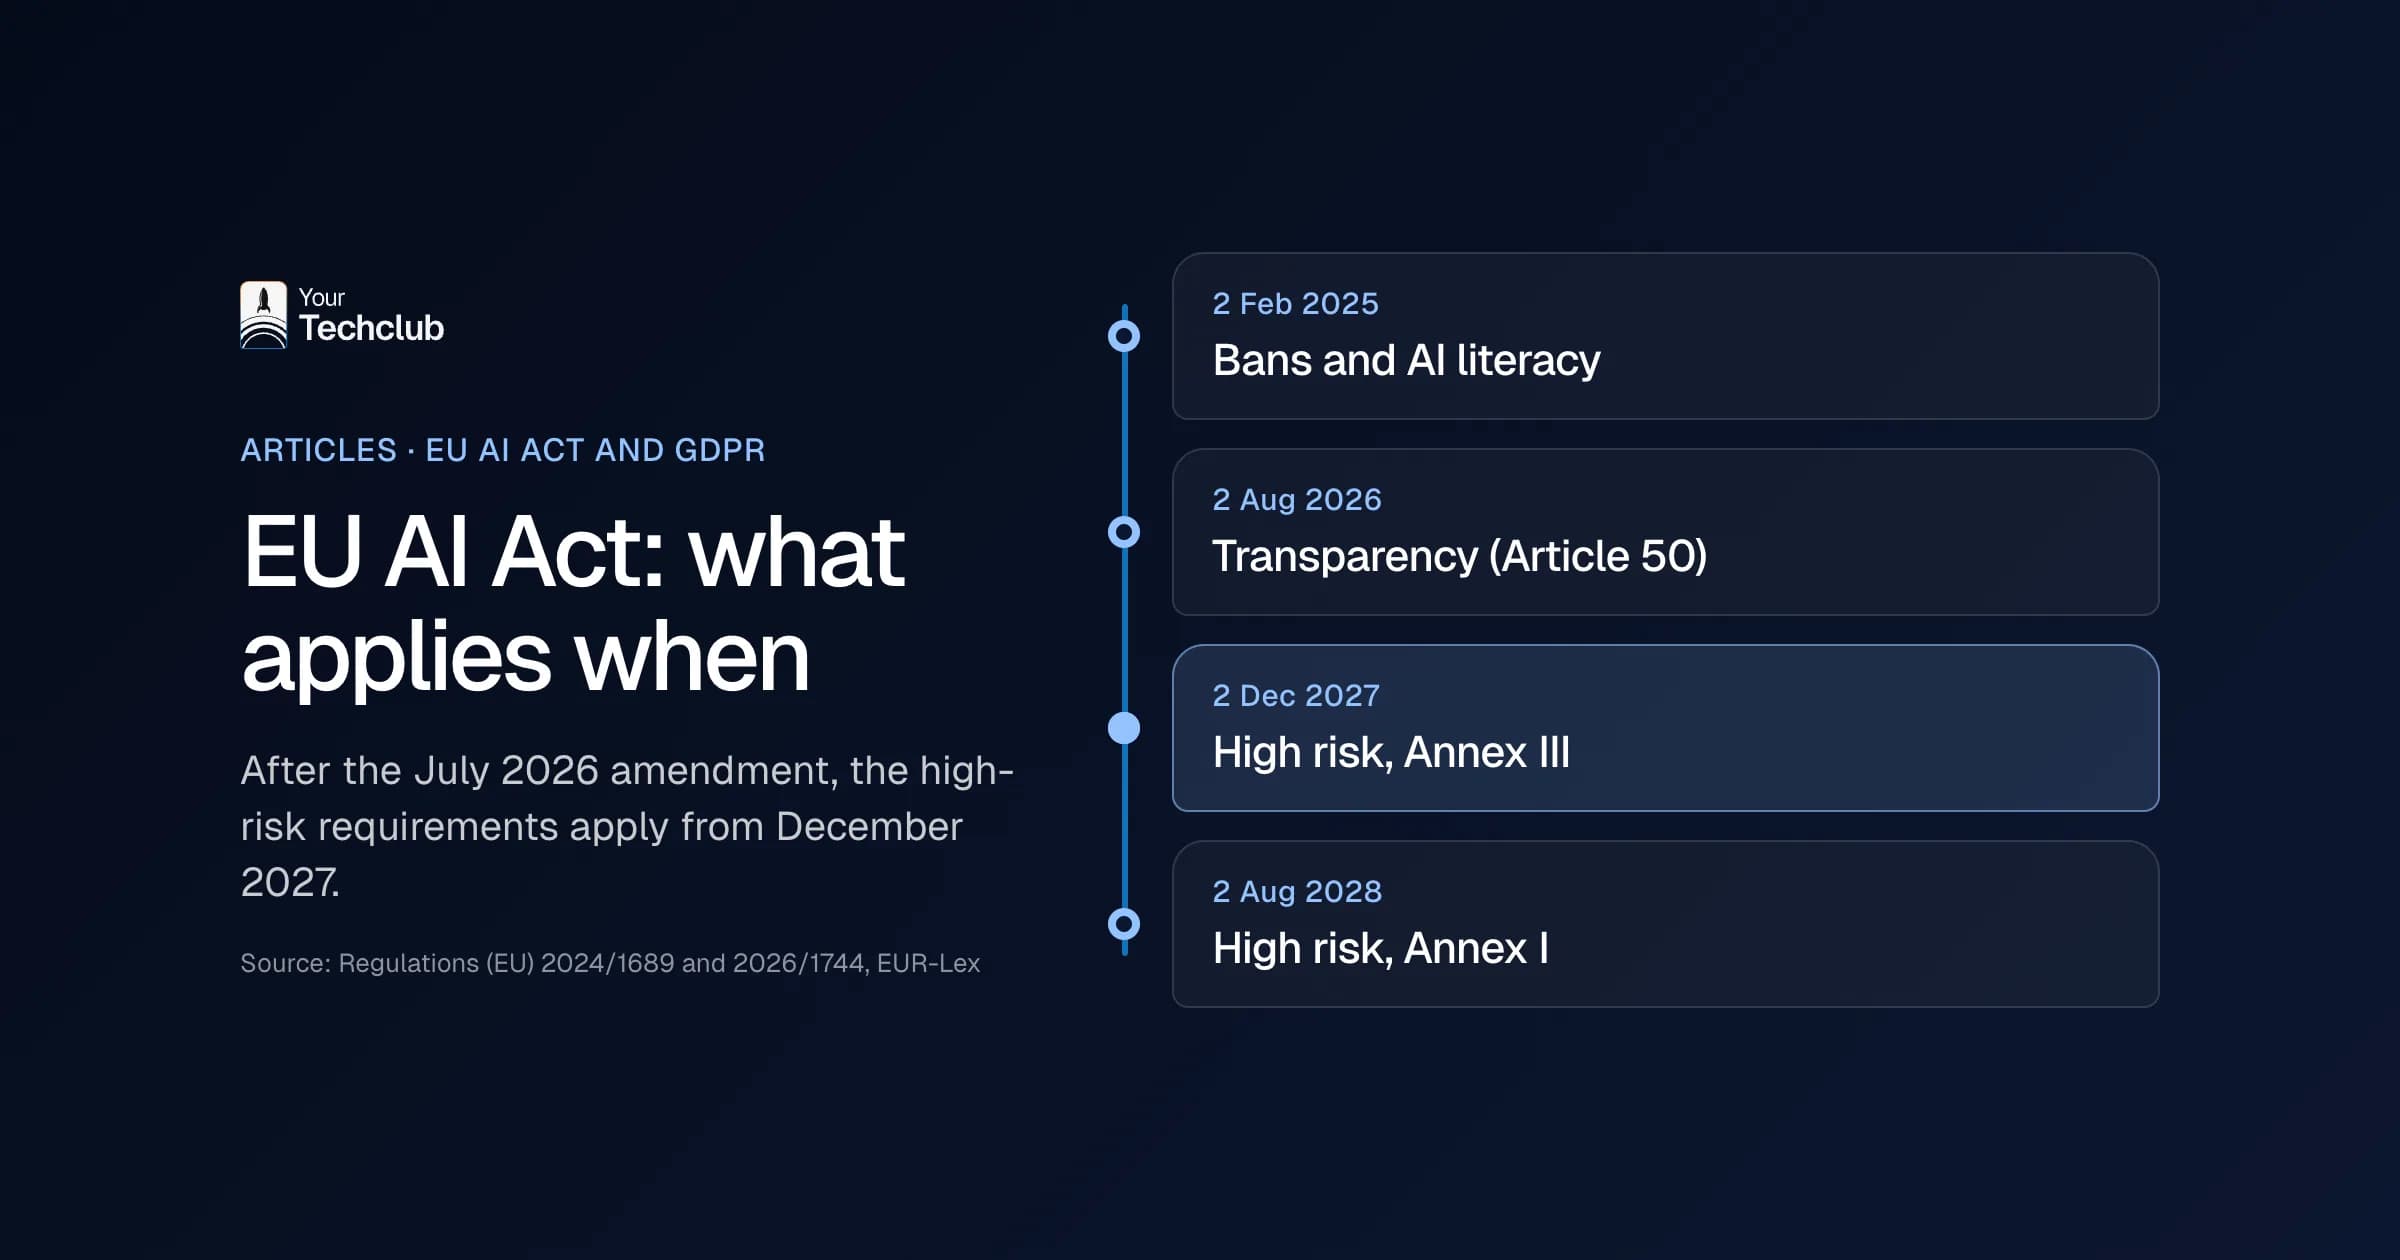
The EU AI Act has been in force since 1 August 2024 and applies in phases. For a typical business, three dates matter: 2 February 2025 for AI literacy and the bans, 2 August 2026 for transparency, and 2 December 2027 for high-risk uses such as recruitment and selection.
| Date | What applies | Who it affects |
|---|---|---|
| 1 August 2024 | The EU AI Act enters into force | Everyone, still without obligations |
| 2 February 2025 | Prohibited practices and AI literacy | Everyone who develops or uses AI |
| 2 August 2025 | Rules for general-purpose AI models | Makers of large models, such as OpenAI and Anthropic |
| 27 July 2026 | Amendment through Regulation 2026/1744 enters into force | Everyone |
| 2 August 2026 | Transparency obligations (Article 50) | Anyone using chatbots or AI-generated content |
| 2 December 2026 | Two new bans, and marking of AI content (Article 50(2)) for generative systems already on the market | Providers of generative AI |
| 2 December 2027 | High-risk requirements (Annex III), such as recruitment and credit | Providers and deployers of those systems |
| 2 August 2028 | Requirements for AI in regulated products (Annex I) | Manufacturers of, for example, medical devices and machinery |
Source: Article 113 of the regulation, as amended by Regulation (EU) 2026/1744, on EUR-Lex. Check the current state before you plan anything, because the regulation will still get implementing rules and guidelines.
Which risk classes does the EU AI Act have?
Four. First, prohibited practices, such as manipulation or social scoring. Then high risk, such as AI in recruitment, credit scoring or access to education. Next, transparency risk, such as chatbots and AI-generated images. Finally, minimal risk, which covers most business uses, for example summarising, sorting email and reading invoices.
| Risk class | Examples | What you need to do |
|---|---|---|
| Prohibited | Social scoring, manipulation, emotion recognition at work (with a few exceptions) | Do not use |
| High risk | Screening CVs, assessing employees, credit scoring, access to education | Risk management, logging, documentation, human oversight, registration |
| Transparency | Chatbot on your website, AI-generated images or texts for the public | Say that it is AI, make AI content recognisable |
| Minimal | Summarising, sorting email, reading invoices, draft texts | Your own policy, AI literacy |
For most SMEs, almost everything falls into the last two rows. The exception is AI in HR. If you use AI to screen CVs, you quickly end up in high risk. What that term means exactly, you can read under high-risk AI.
Are you a provider or a deployer?
If you use an AI system under your own authority, for example an off-the-shelf product as it is, you are a deployer. If you develop an AI system or have one developed, and place it on the market or put it into service under your own name or trademark, you are a provider. Whether you pay for it makes no difference.
Be careful with custom work. If you have an AI agent built to your specification and use it under your own name in your own business, you are usually the provider, not the builder. That follows from the definition in Article 3(3): a provider is also anyone who has an AI system developed and puts it into service under their own name or trademark. For an agent with minimal risk, that adds little work: AI literacy, plus the transparency duties of Article 50 if the agent talks to people or generates content. If the system is high risk, the heavy obligations of Article 16 onwards apply, such as risk management, technical documentation and a conformity assessment. So agree in the contract which documentation and information the builder supplies.
If you buy an off-the-shelf product and use it as it is, you are a deployer (Article 3(4)). With high-risk AI you can still become a provider: if you put your name or trademark on the system, make a substantial modification, or change its intended purpose so that it becomes a high-risk system (Article 25). What the deployer role involves, you can read under deployer.
What does AI literacy ask of your business?
Since 2 February 2025 you have to take measures so that the people who work with AI know enough to do so responsibly. After the July 2026 amendment, this is a duty to take measures that support AI literacy, not a duty to guarantee a set level of knowledge per employee. Think of a short training, house rules and a contact person.
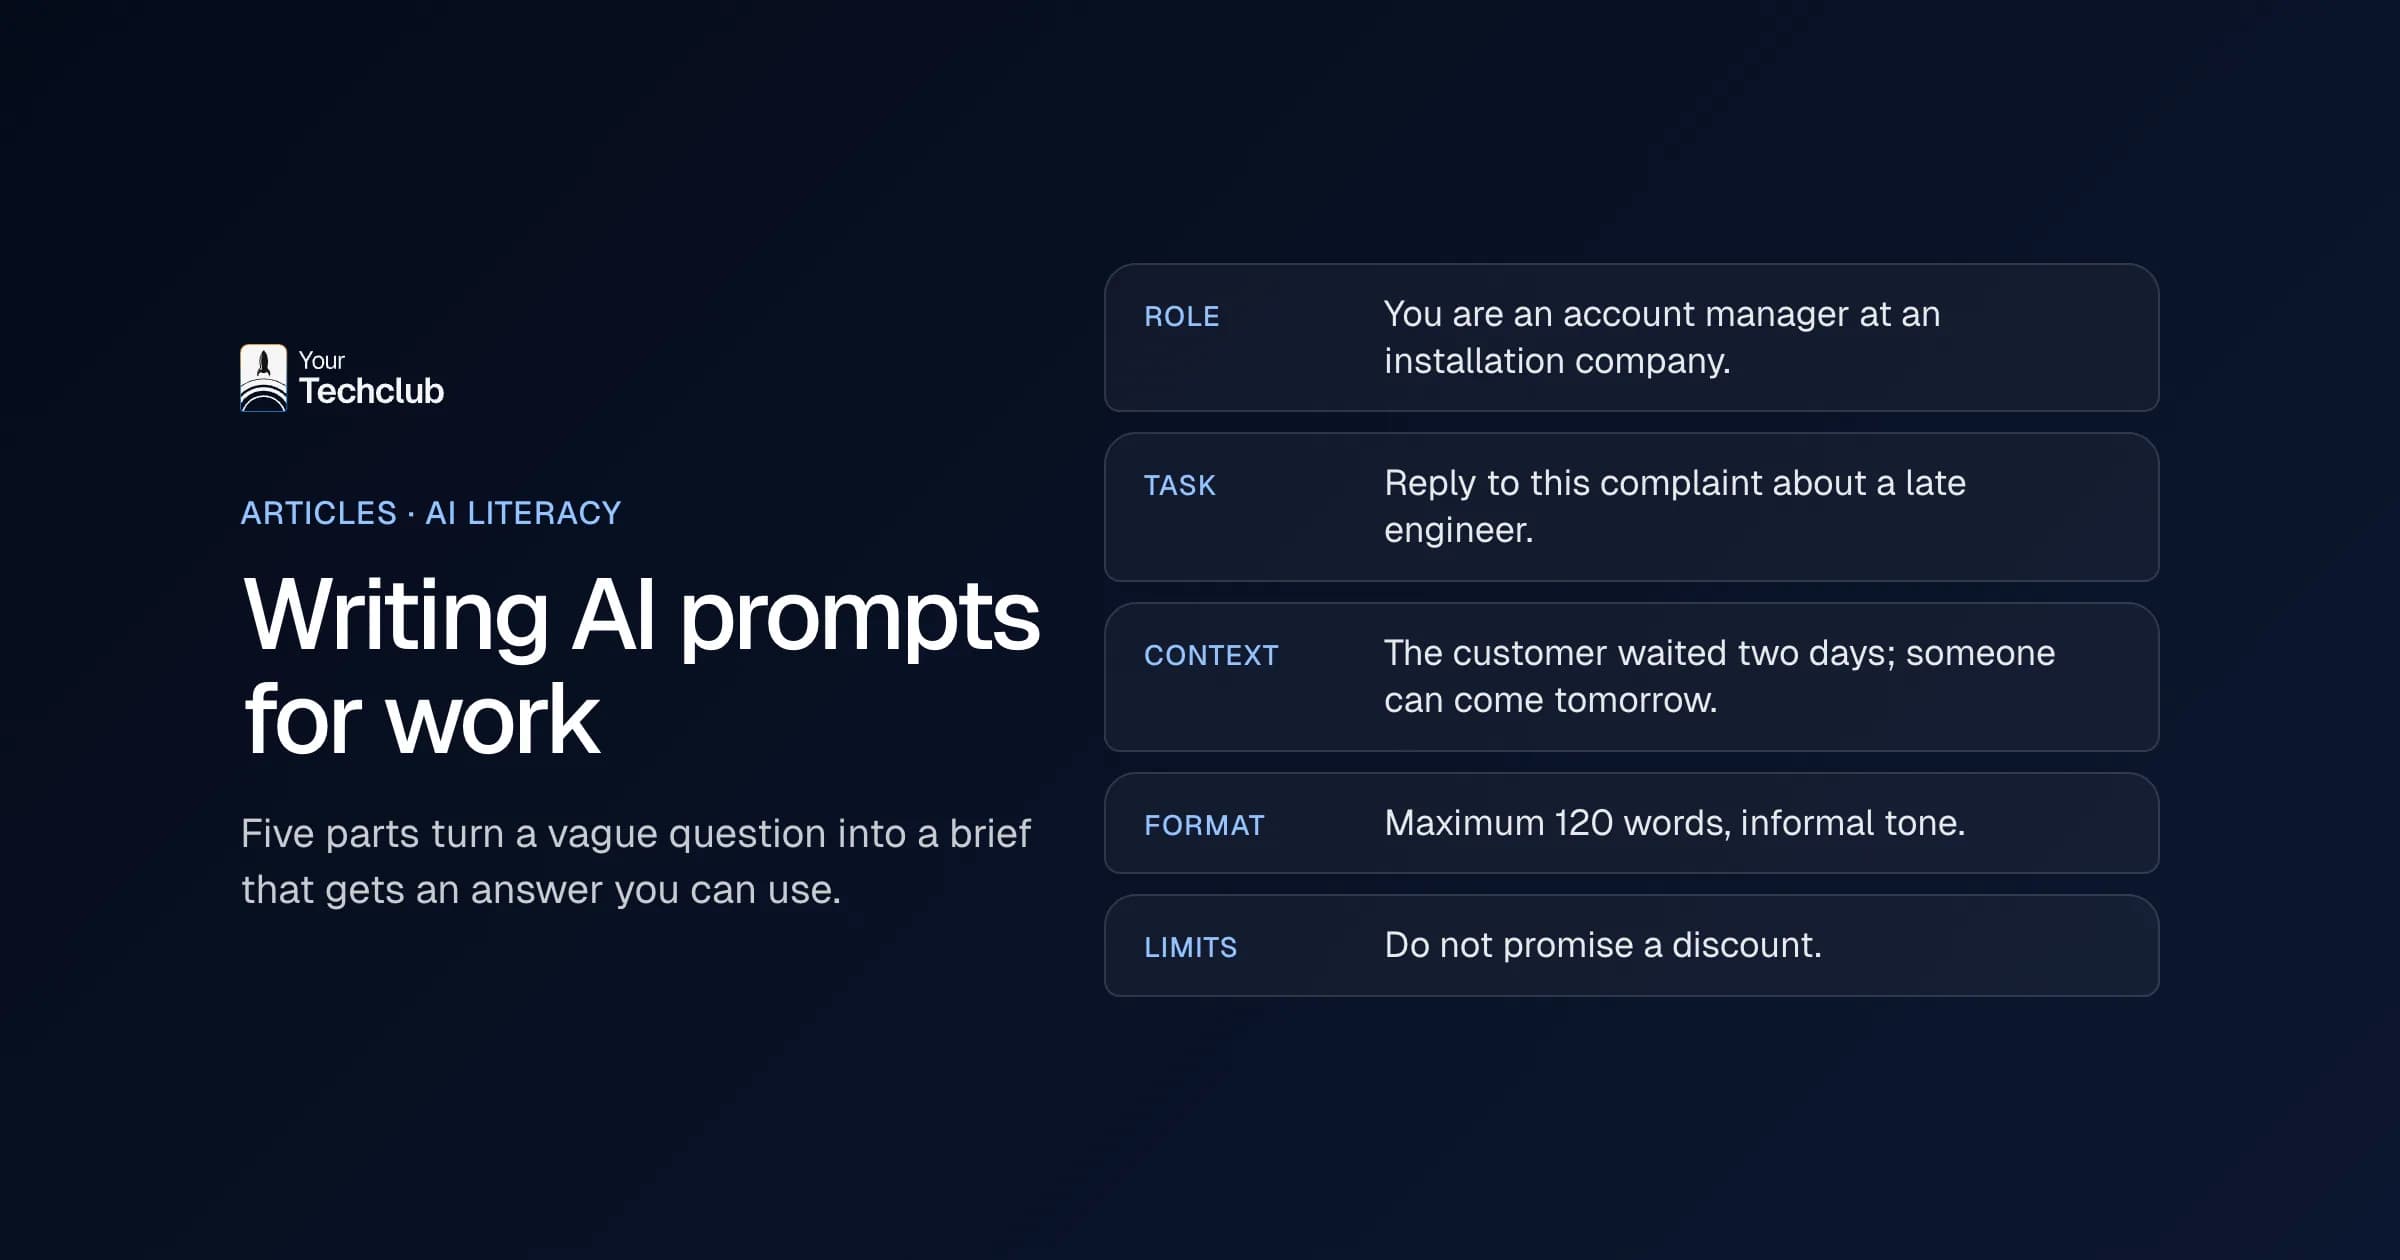
Match the measure to the risk. Someone who only lets AI rewrite texts needs an hour of explanation and one house rule. Someone who uses AI to prepare decisions about customers or staff, however, must know where a model makes mistakes and how to spot them. How to set this up, you can read in the AI literacy requirement and in the short explanation of AI literacy. A practical part of it is learning to give good instructions and to check the answers; that is covered in writing AI prompts.
Where do the GDPR and the EU AI Act overlap?
The GDPR covers personal data, while the EU AI Act covers the AI system itself. As soon as you point AI at CVs, customer files, email or staff data, both apply. They overlap on four points: transparency, human oversight, recording what happens, and agreements with suppliers. So if you sort out those four, you have covered most of both.
Five GDPR points keep coming back with AI:
- Lawful basis: you can explain why you may use this data for this purpose.
- Data minimisation: the model sees no more data than the task needs.
- Transparency: people know that you use AI and what for.
- Automated decisions: extra requirements apply to decisions that a system takes on its own and that significantly affect someone.
- Processors: you sign a data processing agreement with every party that processes data on your behalf.
For uses with a high risk to the people involved, you also need a data protection impact assessment (DPIA). That is work up front, and it saves a lot of discussion afterwards.
How do you tackle the EU AI Act in four steps?
Start with a list of where your company already uses AI, then set the risk per use, record what each system does and who watches it, and finally sort out your supplier agreements. That order works for every business, whatever its size. You do these steps properly once, and after that you repeat them every six months.
Step 1: list where AI is already in use
Start with an inventory, not with a policy. Ask each department which tools they use, including the ones nobody requested. For each use, write down what it does, what data goes in, who uses it and what happens with the result. That list is almost always longer than you expect. For a worksheet, see the shadow AI inventory (Dutch).
Step 2: set the risk for each use
Go through the list with two questions. Does it contain personal data? And does the result lead to a decision about someone? For example, a summary of a public document is something else than a shortlist of job applicants. Put your uses into three boxes: normal use, extra attention, and not without an assessment.
Step 3: record what the system does and who watches it
For every use that goes beyond a simple aid, record what the system does and does not do, which data goes in, who checks the results and how someone can object. Also make sure the system logs things itself: input, sources, result and who approved it. Human oversight means more than an "approve" button. The person who approves must see the reasoning and be able to overrule it.
Step 4: sort out your supplier agreements
Ask every supplier four things. Where do they process and store the data? Do they use it to train models, and can you switch that off? How long do they keep it? And what information do you get so you can meet your own obligations? Then record the answers in the data processing agreement and check them every year.
How to keep track of this without grinding to a halt, you can read in AI governance for SMEs, writing an AI policy and the download AI governance that does not paralyse (Dutch).
What should you watch with ChatGPT and other public models?
The biggest risk is not the model, but the pasting. Someone drops a customer contract or a personnel file into a chat window for a quick summary. So arrange a business environment instead of personal accounts, a short house rule on what may and may not go in, and an alternative that is just as easy. A ban without an alternative simply gets bypassed.
For sensitive data, you can run a model within the EU, or a model you manage yourself. What the business versions cover, you can read in ChatGPT for business and Claude for business. About the risks of made-up answers and misleading input, read preventing AI hallucinations and AI security for SMEs.
What does the EU AI Act mean for AI agents?
An AI agent that takes steps in your systems by itself falls under the same rules as other AI. For most agents, such as sorting email or preparing invoices, that means minimal risk. But if an agent helps decide on recruitment, credit or access to services, it is high risk, with the requirements that apply from 2 December 2027.
My advice: build every agent as if the heavy rules apply. Limits per action, logging out of the agent's reach and a human at irreversible steps cost little extra. They also make an agent easier to manage. If you have the agent custom-built, remember that you are usually the provider (see above). What an agent is exactly, you can read in what is an AI agent.
When can you take this lightly?
If you only use AI on public information or your own non-personal information, and the result never leads to a decision about a person, you are in the lightest category. Think of summarising a public report or drafting an email that you check yourself. In that case, AI literacy and a short house rule are enough.
One A4 page will do: which information may go in, who the contact person is and where to report it when something goes wrong. Nobody reads a thirty-page policy. If you work for or with government, more applies; see public sector and the download AI in public tenders (Dutch).
Who supervises the EU AI Act and what are the fines?
The EU AI Act sets fines of up to EUR 35 million or 7 percent of worldwide annual turnover for prohibited practices, and up to EUR 15 million or 3 percent for other violations (Article 99). For SMEs, the lower of the two amounts applies. In the Netherlands, a separate implementation act decides who supervises; in July 2026 the Public Prosecution Service was still giving advice on it (Openbaar Ministerie, July 2026, in Dutch). Each member state appoints its own supervisors, so check the rules in the country where you operate.
I would not let the fines drive you. For most businesses the real risk is something else: a customer who asks what happens to their data, and you not knowing the answer. Or a tender in which you have to show how you use AI. In both cases the same list from step 1 helps.
What should you do now, and what can wait?
Do these now: arrange AI literacy, list your AI uses and make sure chatbots and AI content are recognisable to customers. All of that already applies. What can wait until it gets closer: the full documentation for high risk, if you have such a use. Still, start on that a year before 2 December 2027.
What I would not do: ban all AI until there is a policy. People will use it anyway, but then in personal accounts and out of your sight. That is exactly the risk the GDPR tries to prevent.
Checklist: the EU AI Act for SMEs
For most businesses, these points cover what the EU AI Act and the GDPR ask of you right now:
- A list of all AI uses, with an owner per use.
- The risk set per use: minimal, transparency or high.
- Your role set per use: provider or deployer.
- AI literacy arranged: training, house rules and a contact person.
- Chatbots and AI content for customers recognisable as AI.
- A data processing agreement with every AI supplier, with training use switched off.
- Logging of input, result and approval for every use that goes beyond a simple aid.
- A human involved in every decision about people.
- For high risk: a plan to meet the requirements before 2 December 2027.
Frequently asked questions
When does the EU AI Act apply?
The EU AI Act has been in force since 1 August 2024 and applies in phases. AI literacy and the bans have applied since 2 February 2025, transparency since 2 August 2026 and the high-risk requirements from 2 December 2027.
Has the EU AI Act been delayed?
Partly. In July 2026 the high-risk requirements moved to 2 December 2027, and those for AI in regulated products to 2 August 2028. AI literacy and the bans still apply.
Does our AI use count as high risk?
That depends on how you use it. The regulation lists, among other things, recruitment and selection, decisions about employees, access to education and credit scoring. If you use AI as an aid for work that a human assesses, the chance is smaller. Have the classification checked by a lawyer.
Can we use ChatGPT for customer data?
Only with agreements in place: a business environment, a written record of where data is processed and whether it is used for training, and a data processing agreement. For sensitive data, you can run a model within the EU.
Are we a provider or a deployer of an AI system?
If you use a system you bought as it is, you are a deployer. If you develop an AI system or have one custom-built, and place it on the market or put it into service under your own name, you are a provider (Article 3(3)). With minimal risk that makes little difference; with high risk, heavy obligations apply.
Sources
- Regulation (EU) 2024/1689 (EU AI Act), including Articles 3 (points 3, 4 and 11), 4, 16, 25, 50, 99 and 113, EUR-Lex
- Regulation (EU) 2026/1744 (Digital Omnibus on AI): new Article 4, amended Article 113 and small mid-caps, EUR-Lex
- AI Omnibus enters into force (27 July 2026), European Commission
- Advice on the Dutch AI Act implementation act (2 July 2026, in Dutch), Openbaar Ministerie